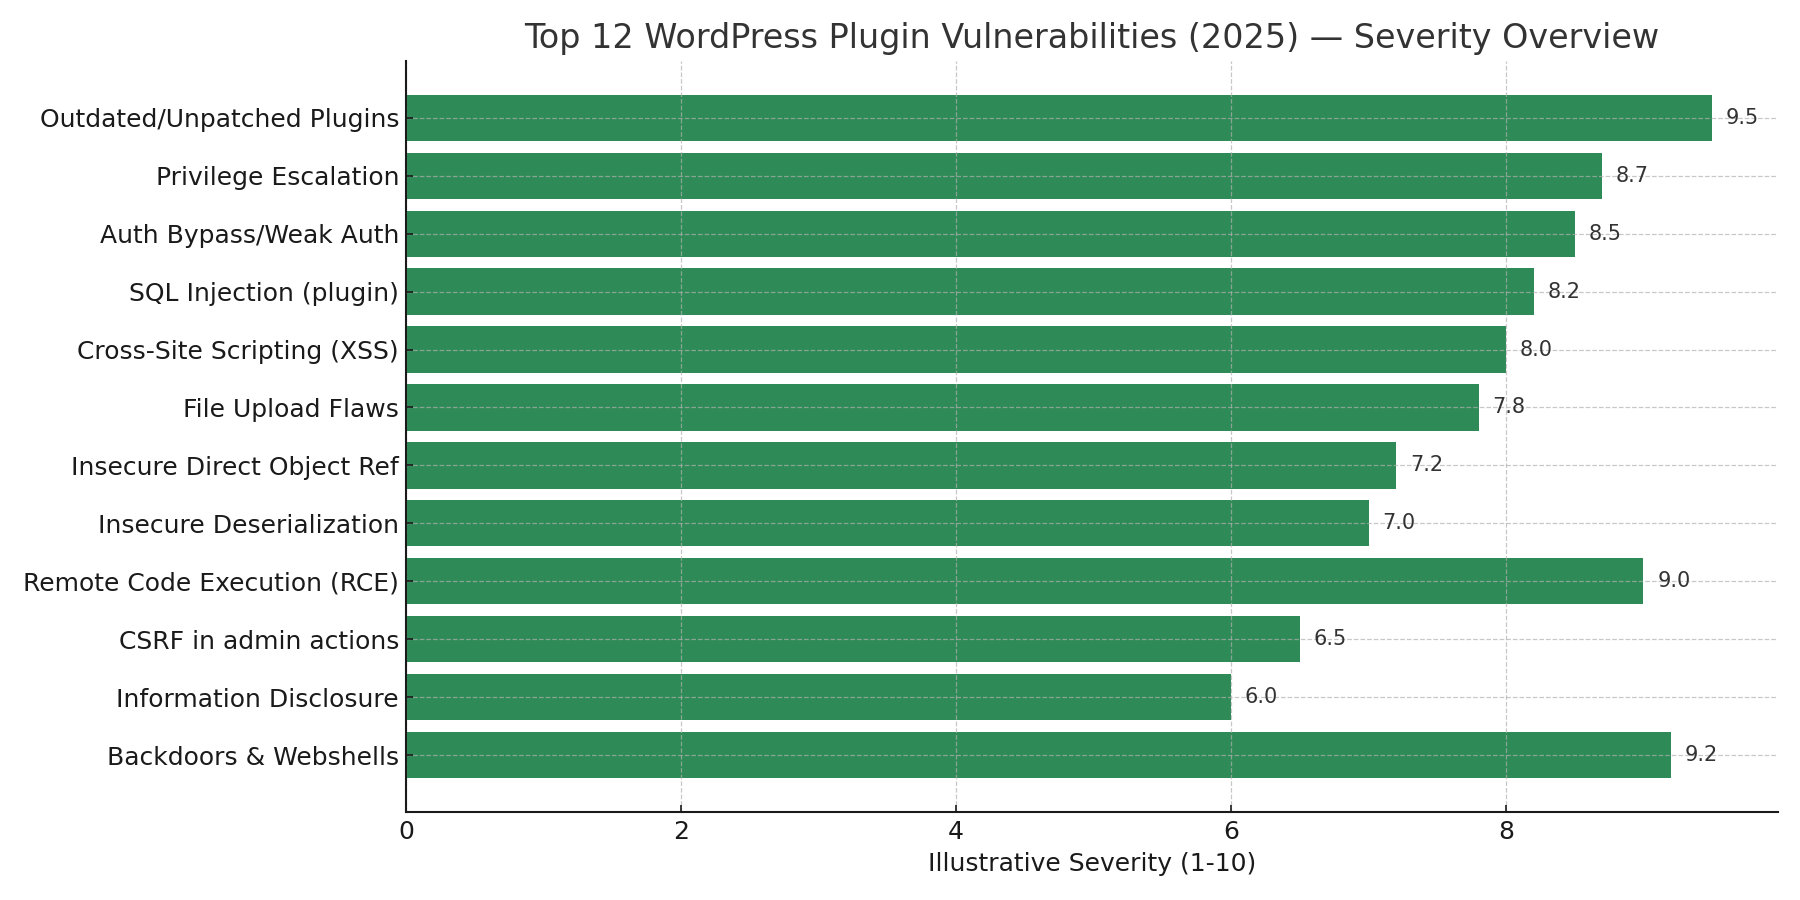
Top 12 WordPress Plugin Vulnerabilities of 2025 — How to Detect and Fix Them

WordPress powers a huge share of the web, and plugins make it flexible — but plugins are also the most common source of site compromises. In 2025 attackers continue to target vulnerable plugins, using automation, supply-chain abuse, and legacy code mistakes to gain access. This guide inventories the Top 12 plugin vulnerabilities, explains how attackers exploit them, provides practical detection scripts and checks you can run today, and gives robust mitigation patterns: from vendor patches to virtual patching with a WAF.

Read More
Hackers Exploiting ICTBroadcast Cookie Flaw (CVE-2025-2611) to Gain Remote Shells — What defenders should know

A critical command-injection bug in ICTBroadcast (an autodialer / call-center platform) — tracked as CVE-2025-2611 (CVSS ~9.3) — is being actively exploited in the wild. Researchers observed attackers using specially crafted HTTP requests that abuse unsafe handling of a session cookie (the BROADCAST cookie) to execute shell commands on exposed servers. Intelligence firms report ~200 internet-facing ICTBroadcast instances appear exposed, with attackers following a two-stage pattern (time-based probe, then attempts to establish reverse shells). Defenders must treat any exposed ICTBroadcast host as high risk and apply containment and remediation steps immediately.

Read More

Beamglea Phishing Infrastructure: 175 Malicious npm Packages Exploited unpkg CDN

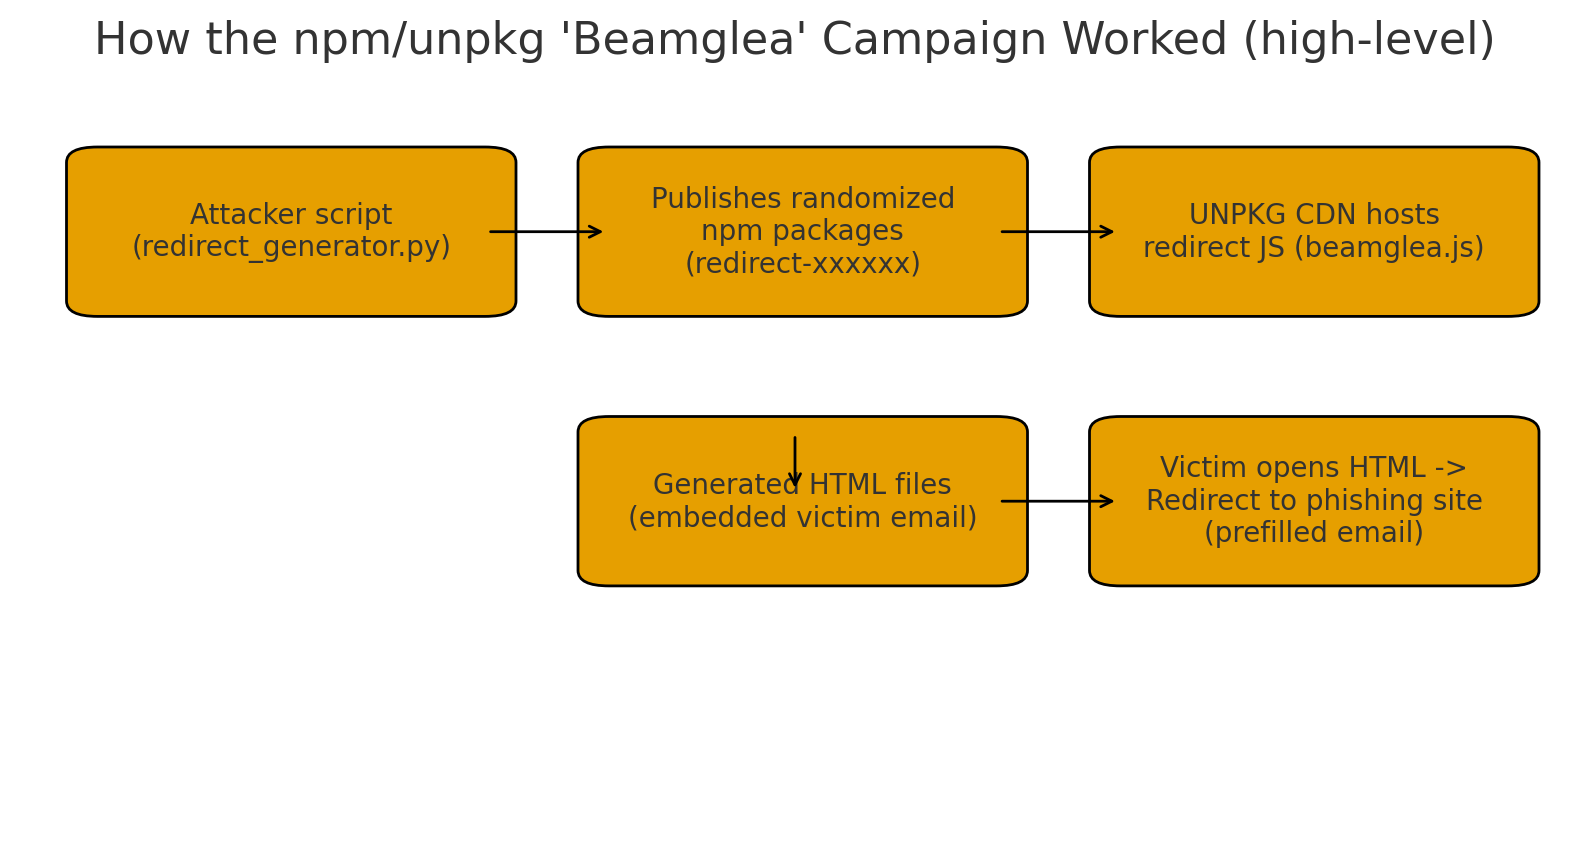
Security teams recently uncovered a coordinated campaign that used hundreds of small npm packages and the unpkg CDN as a free hosting layer for credential-phishing redirects. The operation published dozens of randomized “redirect-xxxxxx” packages and generated tailored HTML files that, when opened by a victim, immediately forwarded them to credential-collection pages with their email pre-filled. According to Socket’s investigation and earlier work by Safety, the set totals roughly 175 malicious npm packages with around 26,000 recorded downloads and infrastructure targeting 135+ organizations.

Read More

Web Security Weekly: Oracle EBS, Redis & WordPress

This weekly digest highlights the highest-priority web security events from Oct 3–10, 2025: a mass extortion campaign abusing Oracle E-Business Suite, a critical Redis RCE, and active WordPress theme compromises that use stealth delivery techniques. Read on for plain-language explanations, key indicators, and a prioritized action plan your team can run in the next 24–72 hours.

Read More

Critical authentication-bypass in Service Finder Bookings being actively exploited — what site owners must do now

A critical authentication-bypass vulnerability in the Service Finder “Bookings” plugin/theme (affecting versions up to 6.0) allows unauthenticated attackers to take over accounts — including administrator accounts — on vulnerable WordPress sites. Multiple security researchers and vendors have confirmed active exploitation in the wild. If your site uses the Service Finder theme or bundled Bookings plugin, update to the fixed release immediately (or remove the plugin) and follow the emergency checklist below.

Read More

Magento (Adobe Commerce / Magento Open Source) — 2025 vulnerability roundup

In 2025 several high-impact vulnerabilities affecting Adobe Commerce and Magento Open Source were publicly disclosed and patched. The most critical is the so-called SessionReaper (CVE-2025-54236) — an improper input validation flaw in the Web API that can lead to session takeover and, in specific conditions, unauthenticated remote code execution. Adobe released an out-of-band hotfix and urged immediate application. Other important 2025 CVEs include a set of access-control and authorization bugs (several CVE entries), and multiple XSS/authorization issues fixed across release updates. Apply vendor patches immediately and follow the detection checklist below.

Read More