Atlassian Patches Critical CVE-2026-21589 in Eight Data Center Products: What Admins Need to Do Now

Atlassian has disclosed a critical path traversal vulnerability affecting eight of its self-hosted Data Center products, including Jira, Confluence and Bitbucket. Tracked as CVE-2026-21589 with a CVSS score of 9.3, the flaw can allow an unauthenticated party to read certain files from the web application root directory.

Atlassian’s cloud-hosted products have already been fixed. Organizations running their own Data Center instances need to update them.

Read More

Zimbra SNMP Flaw CVE-2026-73570 Exploited to Plant Web Shells and Steal Mailbox Data

Attackers are exploiting a now-patched vulnerability in Zimbra Collaboration Suite (ZCS) to deploy web shells and gain access to mailbox data, according to the Microsoft Security Research team.

The flaw, tracked as CVE-2026-73570 (CVSS score: 8.9), is an unauthenticated operating system command injection that can lead to remote code execution. The server is exposed when SNMP notifications are enabled and the optional zimbra-snmp package is installed. An attacker only needs to send a specially crafted SMTP request — in other words, an email — to an internet-facing Zimbra server. No authentication or user interaction is required. Zimbra fixed the issue in July 2026 with version 10.1.20.

Read More

The Official MCP Python SDK Leaked OAuth Credentials to Malicious Servers. If You Connect to Third-Party MCP Servers, Patch and Rotate

A flaw in the official MCP (Model Context Protocol) Python SDK let a malicious MCP server steal the OAuth credentials of any client that connected to it. Not a low-value session token, but client secrets, authorization codes, and PKCE proof keys, enough to mint valid access tokens with the full permissions of the connecting application. The root cause is simple and old: the SDK sent credentials without first verifying who it was sending them to. Cycode reported it, along with seven other credited researchers, and the fix landed in SDK versions 1.30.0 and 2.2.0.

MCP is how AI agents plug into external tools and services, and it is spreading fast into exactly the kind of automation that runs on servers and in build pipelines. If any of your systems act as an MCP client and connect to servers you do not fully control, this is a credential-theft problem you need to close now, and patching alone does not finish the job.

Read More

Two Citrix NetScaler RCE Flaws: From Unpatched Zero-Days to CISA-Confirmed Exploitation in a Day

If you have a Citrix NetScaler ADC or NetScaler Gateway on your perimeter, this is a patch-today situation. Over the weekend the story moved from “two unpatched zero-days being exploited before any fix existed” to “CISA confirms global exploitation, CVEs assigned, added to the catalog, patches out.” Both flaws are unauthenticated remote code execution on a device that by definition faces the internet and sits in front of your entire internal network.

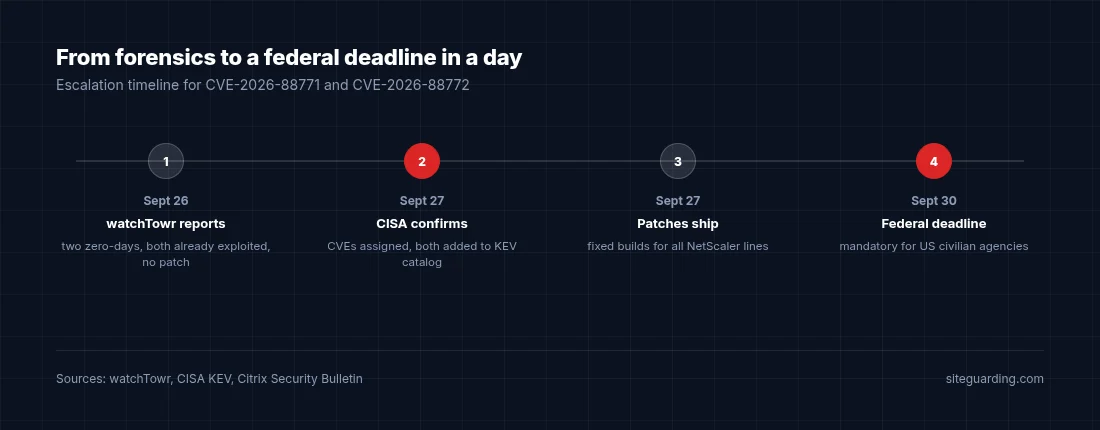
Timeline: September 26 watchTowr reports two unpatched zero-days in NetScaler, September 27 CISA confirms exploitation and adds them to the KEV catalog, September 30 deadline for US federal civilian agencies

Read More