
FortiMail Zero-Day (CVE-2026-104286, CVSS 9.8): No Patch Yet, Actively Exploited
Zimbra SNMP Flaw CVE-2026-73570 Exploited to Plant Web Shells and Steal Mailbox Data
Attackers are exploiting a now-patched vulnerability in Zimbra Collaboration Suite (ZCS) to deploy web shells and gain access to mailbox data, according to the Microsoft Security Research team.
The flaw, tracked as CVE-2026-73570 (CVSS score: 8.9), is an unauthenticated operating system command injection that can lead to remote code execution. The server is exposed when SNMP notifications are enabled and the optional zimbra-snmp package is installed. An attacker only needs to send a specially crafted SMTP request — in other words, an email — to an internet-facing Zimbra server. No authentication or user interaction is required. Zimbra fixed the issue in July 2026 with version 10.1.20.
OpenSSL Patches a High-Severity DTLS Flaw (CVE-2026-84782) That Can Leak Server Memory to Remote Peers
The Official MCP Python SDK Leaked OAuth Credentials to Malicious Servers. If You Connect to Third-Party MCP Servers, Patch and Rotate
A flaw in the official MCP (Model Context Protocol) Python SDK let a malicious MCP server steal the OAuth credentials of any client that connected to it. Not a low-value session token, but client secrets, authorization codes, and PKCE proof keys, enough to mint valid access tokens with the full permissions of the connecting application. The root cause is simple and old: the SDK sent credentials without first verifying who it was sending them to. Cycode reported it, along with seven other credited researchers, and the fix landed in SDK versions 1.30.0 and 2.2.0.
MCP is how AI agents plug into external tools and services, and it is spreading fast into exactly the kind of automation that runs on servers and in build pipelines. If any of your systems act as an MCP client and connect to servers you do not fully control, this is a credential-theft problem you need to close now, and patching alone does not finish the job.
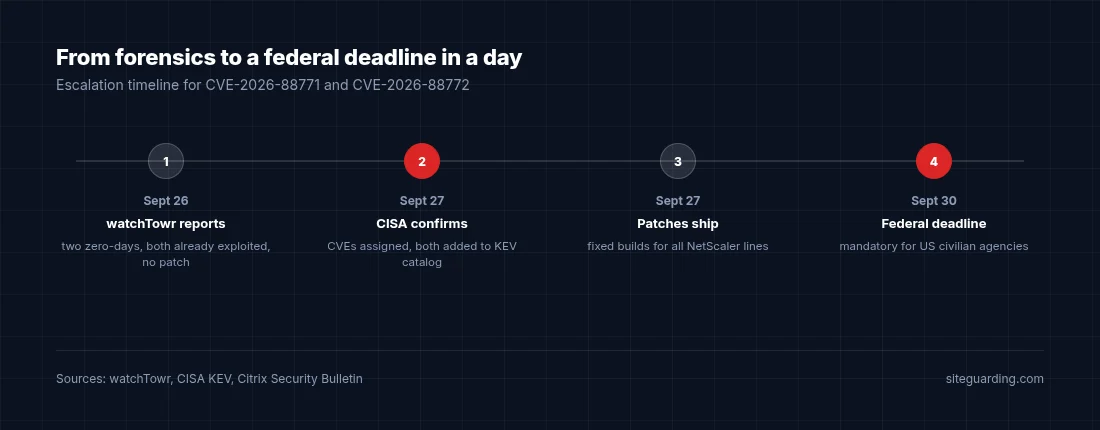
Two Citrix NetScaler RCE Flaws: From Unpatched Zero-Days to CISA-Confirmed Exploitation in a Day
If you have a Citrix NetScaler ADC or NetScaler Gateway on your perimeter, this is a patch-today situation. Over the weekend the story moved from “two unpatched zero-days being exploited before any fix existed” to “CISA confirms global exploitation, CVEs assigned, added to the catalog, patches out.” Both flaws are unauthenticated remote code execution on a device that by definition faces the internet and sits in front of your entire internal network.
Roundcube Pre-Auth SQL Injection (CVE-2026-48842): Patched in May, Being Exploited Now
If you run Roundcube webmail, or your hosting provider does, this one needs attention today. CVE-2026-48842 is a pre-authentication SQL injection in Roundcube that an attacker can hit with no login at all, and it is under active exploitation in the wild. Roundcube shipped the fix back in May 2026. The problem is the gap between “patch exists” and “patch applied,” and on shared hosting that gap is exactly where webmail installs sit and rot.
We clean up compromised hosting environments for a living, and webmail is one of the most reliably neglected surfaces on any server. It gets installed once, exposed to the internet permanently, and then nobody touches it until something goes wrong. That is the population getting hit right now.
Malware Reaches the Terraform Registry: DPRK-Linked Actors Turn Your IaC Pipeline Into a Delivery Channel
For the first time, attackers have used HashiCorp’s public Terraform Registry to distribute malware. Two malicious Terraform providers and two Go modules delivered a Go-based implant that talks to its operators over a blockchain smart contract and a Slack bot, and the campaign links back to Graphalgo, a North Korea-attributed operation first documented in February. The provider counts are small so far, but the vector is the story: if a poisoned dependency can enter through your infrastructure-as-code, it enters with a direct line to your production credentials.
We spend a lot of time on the seam between deployment tooling and live infrastructure, and this is exactly the seam attackers are now probing. A malicious npm package infects a developer laptop. A malicious Terraform provider runs inside the process that provisions your cloud. Those are not the same blast radius.
MikroTrick: Two RouterOS Bugs Chained Into a Full Admin Takeover With No Password at All
Attackers were taking full administrative control of Internet-facing MikroTik routers over SSH without a password, without an SSH key, and without ever completing authentication. The chain, named MikroTrick by CERT Polska, was being used in the wild at least a day before MikroTik shipped patches. If a MikroTik router sits in front of your servers or hosting infrastructure, this is one to take seriously, because a compromised edge router is not just a compromised router. It is a foothold in front of everything behind it.
We see MikroTik gear constantly on the perimeter of hosting setups and server infrastructure we manage, and the reason this attack matters is that the router is the one device that sees all your traffic and holds the keys to your network layout. Here is how the chain works, how to tell if you were hit, and what to do about it.
The MemTensor Supply Chain Compromise: How Two Poisoned Packages Turned Into a Self-Spreading Credential Stealer
An attacker quietly pushed malicious versions of two legitimate MemTensor packages onto npm and PyPI, and anyone who installed the wrong version handed over their cloud keys, registry tokens, source-code access, and developer secrets. The payload is a Go-based stealer called sckit, and the ugly part is that it behaves like a worm: it carries the templates to reinstall itself into other npm packages, Python packages, and GitHub Actions workflows. This is not “a bad package got published.” This is a supply chain attack that tries to keep spreading through whoever it lands on.
We deal with the fallout of compromised developer machines and deployment pipelines regularly, and this one is worth understanding in detail because the delivery method, stealing a project’s own publishing tokens, is becoming the standard playbook. If your site’s build or deploy touches npm or PyPI, read the indicators below and check yourself today.